COMPTIA · CAS-005

CompTIA SecurityX CAS-005 Exam Practice Questions

475 questionsInstant PDF downloadUpdated September 2026

US$39

Try 10 questions free

Card, Apple Pay or Google Pay. Your PDF is sent by email as soon as you check out.

Pass or your money backFail the exam after using this pack and we refund it. How the guarantee works
Category:
TRY BEFORE YOU BUY

Three of the 475 questions in this pack

Question 1

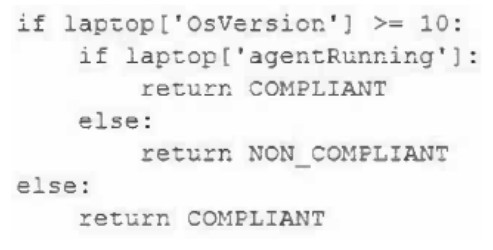
A security engineer is reviewing event logs because an employee successfully connected a personal Windows laptop to the corporate network, which is against company policy. Company policy allows all Windows 10 and 11 laptops to connect to the system as long as the MDM agent installed by IT is running. Only compliant devices can connect, and the logic in the system to evaluate compliant laptops is as follows: Which of the following most likely occurred when the employee connected a personally owned Windows laptop and was allowed on the network?

Exhibit for question 1

  1. The agent was not running on the laptop, which triggered a false positive.
  2. The OS was a valid version, but the MDM agent was not installed, triggering a true positive.
  3. The OS was running a Windows version below 10 and triggered a false negative.
  4. The OS version was higher than 11, and the MDM agent was running, triggering a true negative. ✅Correct Answer: C, The OS was running a Windows version below 10 and triggered a false negative. The device is reported COMPLIANT only when OsVersion >= 10 and agentRunning is true; otherwise the inner branch returns NON_COMPLIANT. A personal laptop that reached the network was wrongly passed, so the check produced a false negative: it reported COMPLIANT for a device that should have been blocked. That happens when OsVersion is below 10, because the outer test fails, the agentRunning check is skipped entirely, and control falls to the final else, which returns COMPLIANT. The outdated OS does not meet policy, but the logic error lets it connect anyway.
Show answer and explanation

The answer and explanation for this question are in the free sample PDF.

Question 2

An organization is working to secure its development process to ensure developers cannot deploy artifacts directly into the production environment. Which of the following security practice recommendations would be the best to accomplish this objective?

  1. Implement least privilege access to all systems.
  2. Roll out security awareness training for all users.
  3. Set up policies and systems with separation of duties.
  4. Enforce job rotations for all developers and administrators.
  5. Utilize mandatory vacations for all developers.
  6. Review all access to production systems on a quarterly basis.
Show answer and explanation

Correct answer: C. Set up policies and systems with separation of duties.

Separation of duties is a fundamental access control principle that prevents any single individual from having complete control over a critical transaction or process. By implementing policies and systems with separation of duties, the organization ensures that developers cannot unilaterally deploy artifacts to production, this requires approval and execution by different roles. This directly addresses the stated objective of preventing direct production deployments by developers.

Why the other options are wrong

  • A. Least privilege access is important but doesn't specifically prevent developers from deploying to production if they have any production access.
  • B. Security awareness training improves security culture but doesn't enforce technical controls preventing direct deployments.
  • D. Job rotation reduces insider threat risk over time but doesn't prevent current deployment capabilities.
  • E. Mandatory vacations may help detect fraudulent activities but don't prevent unauthorized deployments.
  • F. Quarterly access reviews are detective controls that occur too infrequently to prevent unauthorized deployments.

Question 3

A security architect discovers the following while reviewing code for a company's website: selection = "SELECT Item FROM Catalog WHERE ItemID = " & Request("ItemID") Which of the following should the security architect recommend?

  1. Client-side processing
  2. Query parameterization
  3. Data normalization
  4. Escape character blocking
  5. URL encoding
Show answer and explanation

Correct answer: B. Query parameterization

The code is vulnerable to SQL injection because user input from Request('ItemID') is concatenated straight into the query string. Query parameterization, also called prepared statements, sends the SQL structure and the user-supplied values separately, so input is treated as data and never as executable SQL. This is the primary, industry-standard defense against SQL injection.

Why the other options are wrong

  • A. Client-side processing can be bypassed by any attacker crafting requests directly, and the injection still executes at the database.
  • C. Data normalization organizes how data is stored; it does not separate code from input in a query.
  • D. Blocking or escaping characters is a filtering approach that is incomplete and can be bypassed by alternate encodings.
  • E. URL encoding only changes how characters are represented in a request; the database still executes the injected SQL.

See all 10 free questions Get the full pack, US$39

475 practice questions for CompTIA SecurityX (CAS-005), MCQs and PBQs, with full explanations.

Every multiple choice and performance-based question comes with the correct answer, a clear explanation, and a note on why each other option is wrong. Work through it once with the answers, then again with the questions-only copy under exam conditions.

  • 475 questions, MCQs and PBQs, mapped to the CAS-005 exam objectives
  • Answers and explanations for every question, including the wrong options
  • A questions-only PDF for timed practice runs
  • Instant delivery by email the moment you check out
  • Free monthly updates for as long as the exam is live
  • Pass or your money back

A SecurityX voucher costs US$544, CompTIA’s most expensive exam. This pack is US$39, paid once.

Try 10 questions free before you buy.

Last updated September 2026 · 475 questions

What makes the SecurityX hard

Fail it and CompTIA charges the full US$544 again, the most expensive exam in its catalogue. SecurityX is not multiple choice only: performance based questions put you inside real security scenarios and expect you to make the call, not just recognise the right term.

It is also scored pass or fail only. There is no scaled score and no partial credit, so a near miss counts the same as a wide one, and there is no score report telling you how close you came.

This is CompTIA’s most advanced cybersecurity certification, the former CASP+ rebranded and expanded, and it is DoD 8140/8570 approved at expert level. For a large share of senior government and defence roles that approval is not optional, it is required. This pack puts all 475 questions, MCQ and PBQ, in one place, so the scenario framing is familiar before exam day.

About the exam

CompTIA SecurityX is CompTIA’s most advanced cybersecurity certification, formerly CASP+ and rebranded as part of the Xpert series. It validates expert level skills in security architecture, engineering, governance, risk and compliance, and security operations across complex enterprise environments including cloud, hybrid and on-premises. It is DoD 8140/8570 approved and is treated as a direct competitor to CISSP and CISM for senior security roles. The current version is V5, series code CAS-005, launched 17 December 2024. Ten years of IT experience including five years of hands-on security experience is recommended.

Exam domains

  • Governance, risk and compliance: 20%
  • Security architecture: 27%
  • Security engineering: 31%
  • Security operations: 22%

Up to 90 questions including PBQs, up to 165 minutes, pass or fail only, no scaled score, Pearson VUE testing centres or online proctored, US$544 per voucher, valid for three years.
Reviews

There are no reviews yet.

Only logged in customers who have purchased this product may leave a review.

Questions before you buy

What do I get when I buy the CompTIA SecurityX CAS-005 pack?

475 practice questions as a PDF, each with the correct answer, a full explanation and a note on why the other options are wrong, plus a separate questions-only PDF for timed practice.

How quickly do I receive it?

Straight away. The full PDF and a questions-only copy are emailed to you the moment your payment goes through, and the same links are on your order page.

Is there a free sample?

Yes. Ten questions from this pack, with answers and explanations, are free on this page and as a PDF, so you can judge the quality before you pay.

Are updates included?

Yes. The pack is updated every month for as long as the exam is live, and updates are free for everyone who has bought it.

What if I fail the exam?

We refund the pack. Sit the exam 7 to 30 days after buying, then send your official score report within 7 days of the exam date, as set out in the refund policy.

Can I share it with colleagues?

Each purchase is licensed to one person. For a team, school or training organisation, email support@certstash.com for a licence that fits.