MICROSOFT · MD-102

Microsoft MD-102 Exam Practice Questions

409 questionsInstant PDF downloadUpdated September 2026

US$39

Try 10 questions free

Card, Apple Pay or Google Pay. Your PDF is sent by email as soon as you check out.

Pass or your money backFail the exam after using this pack and we refund it. How the guarantee works
Category:
TRY BEFORE YOU BUY

Three of the 409 questions in this pack

Question 1

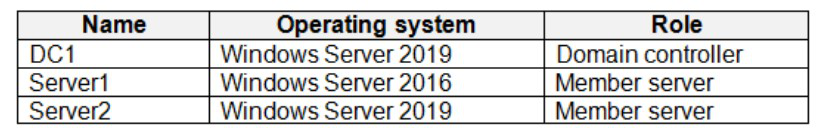
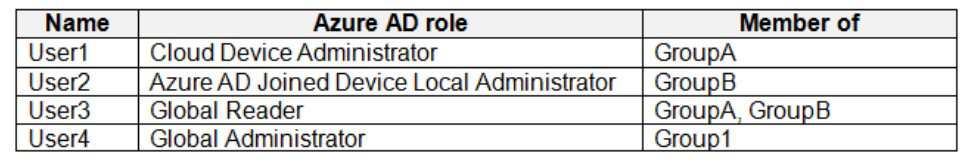
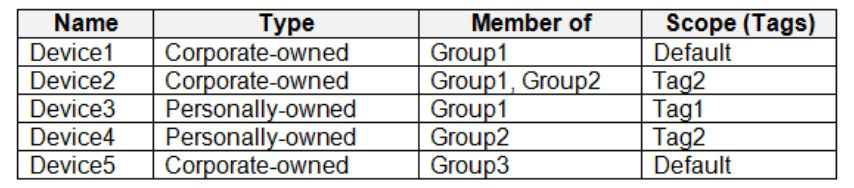
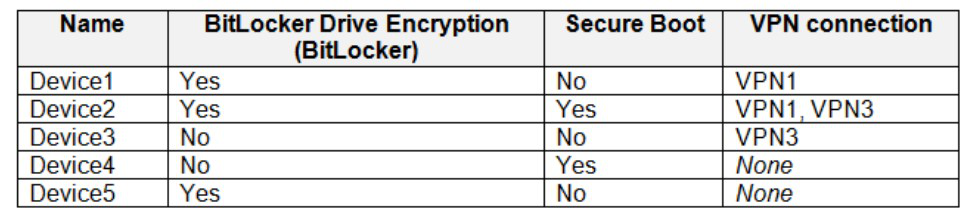
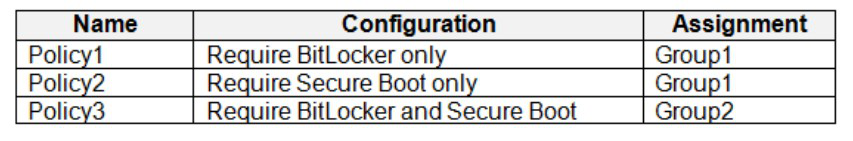
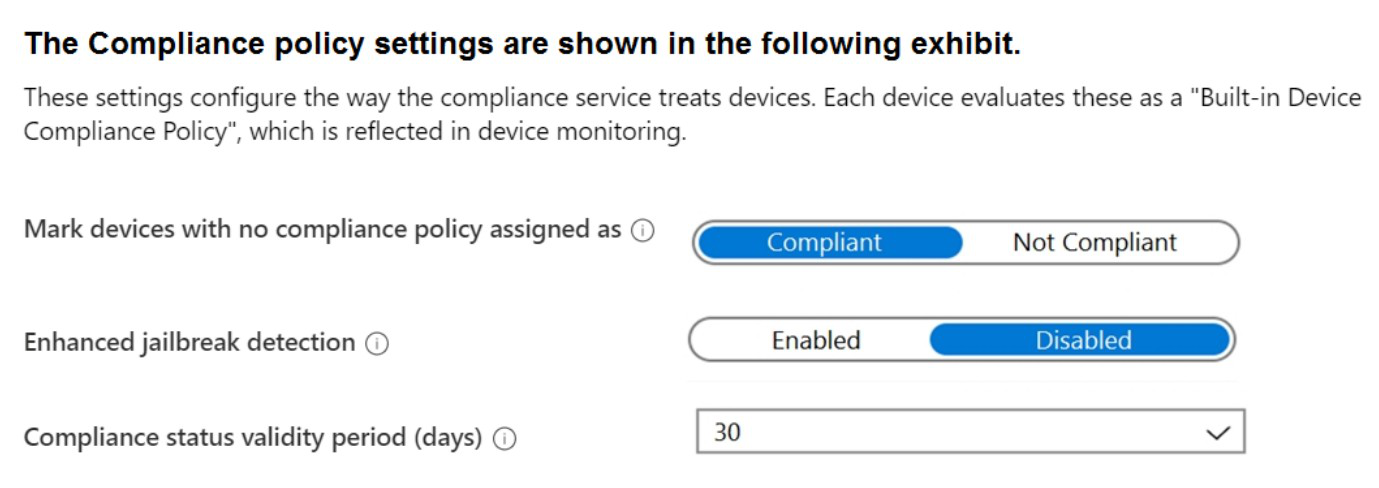
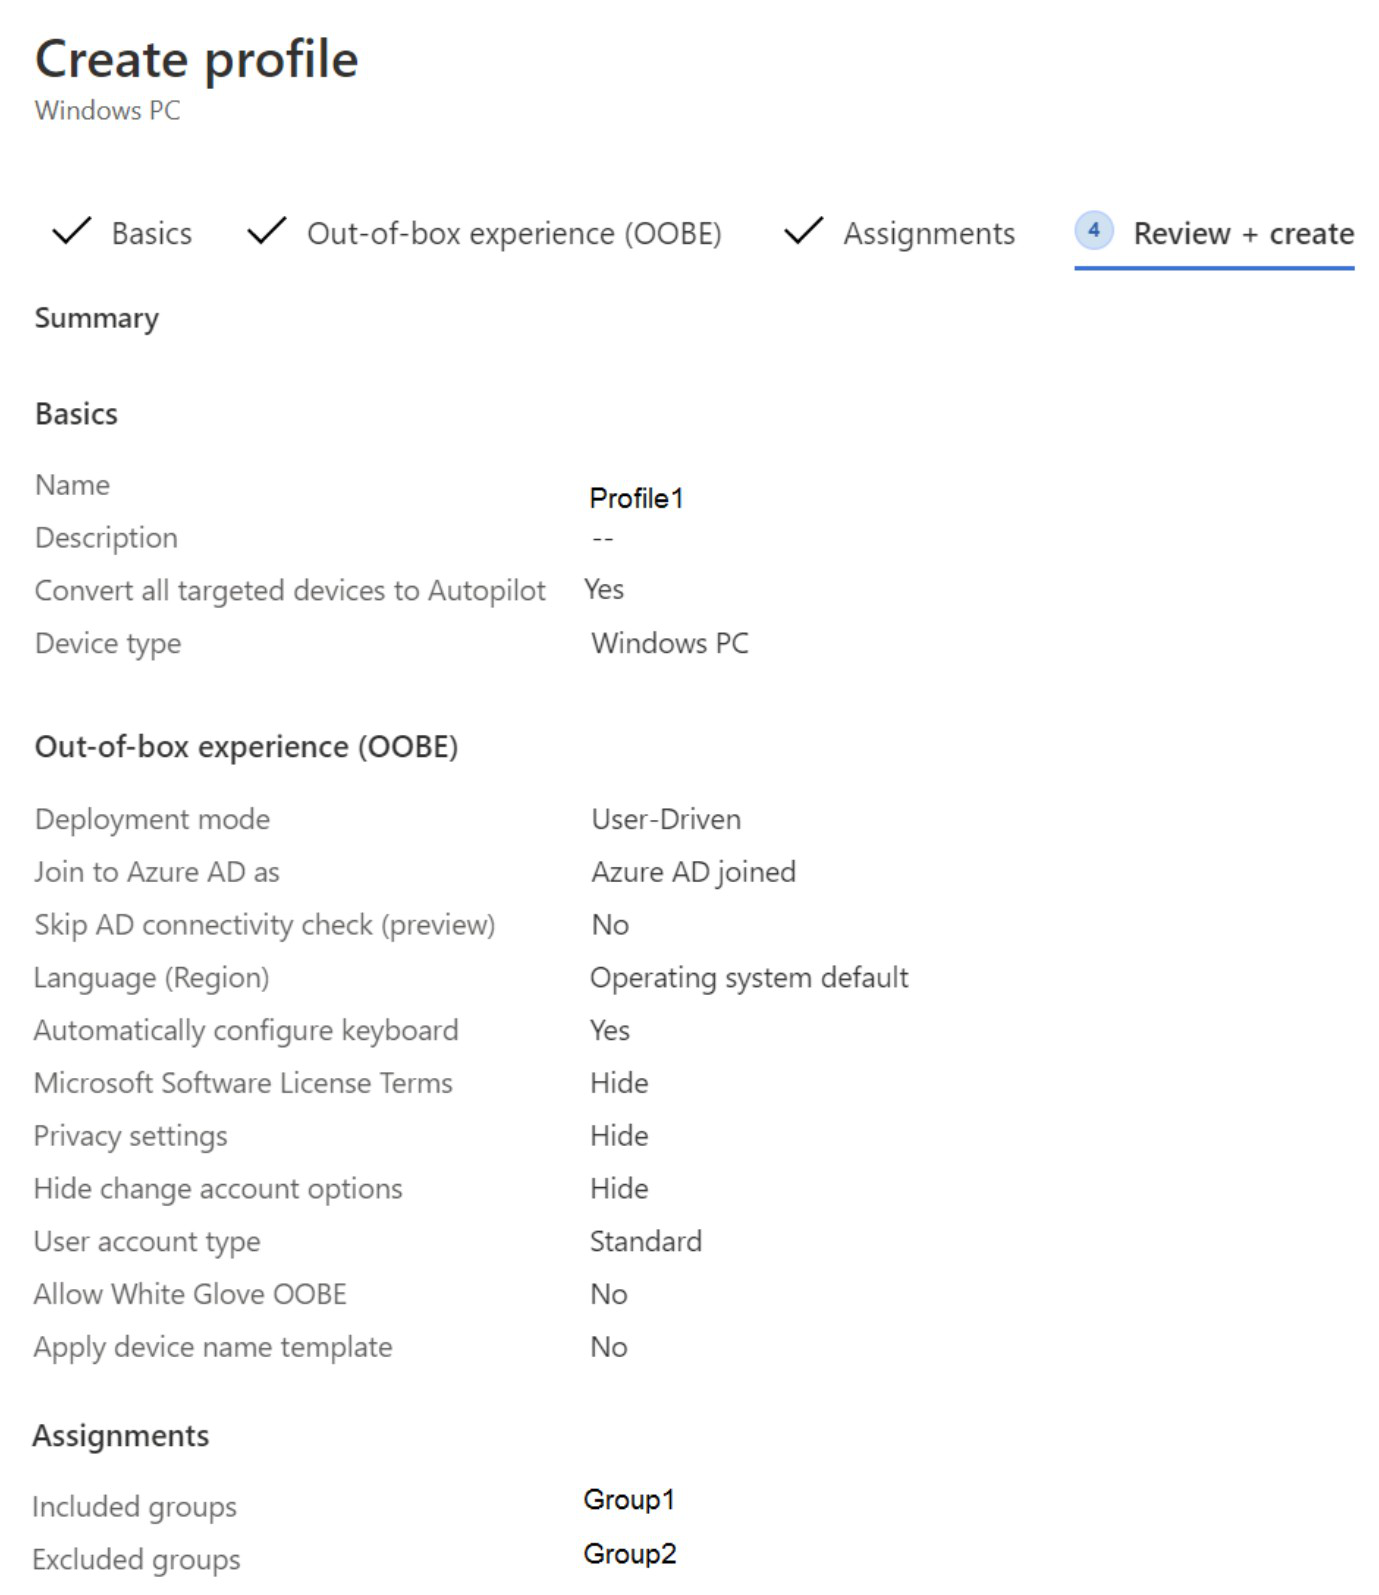
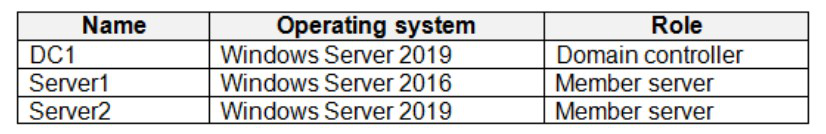
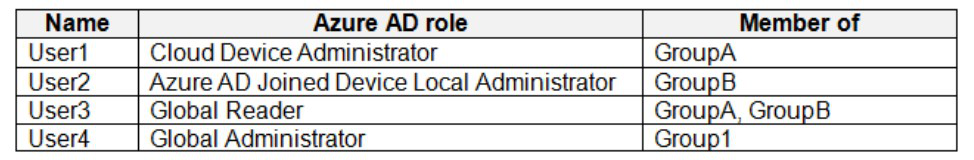
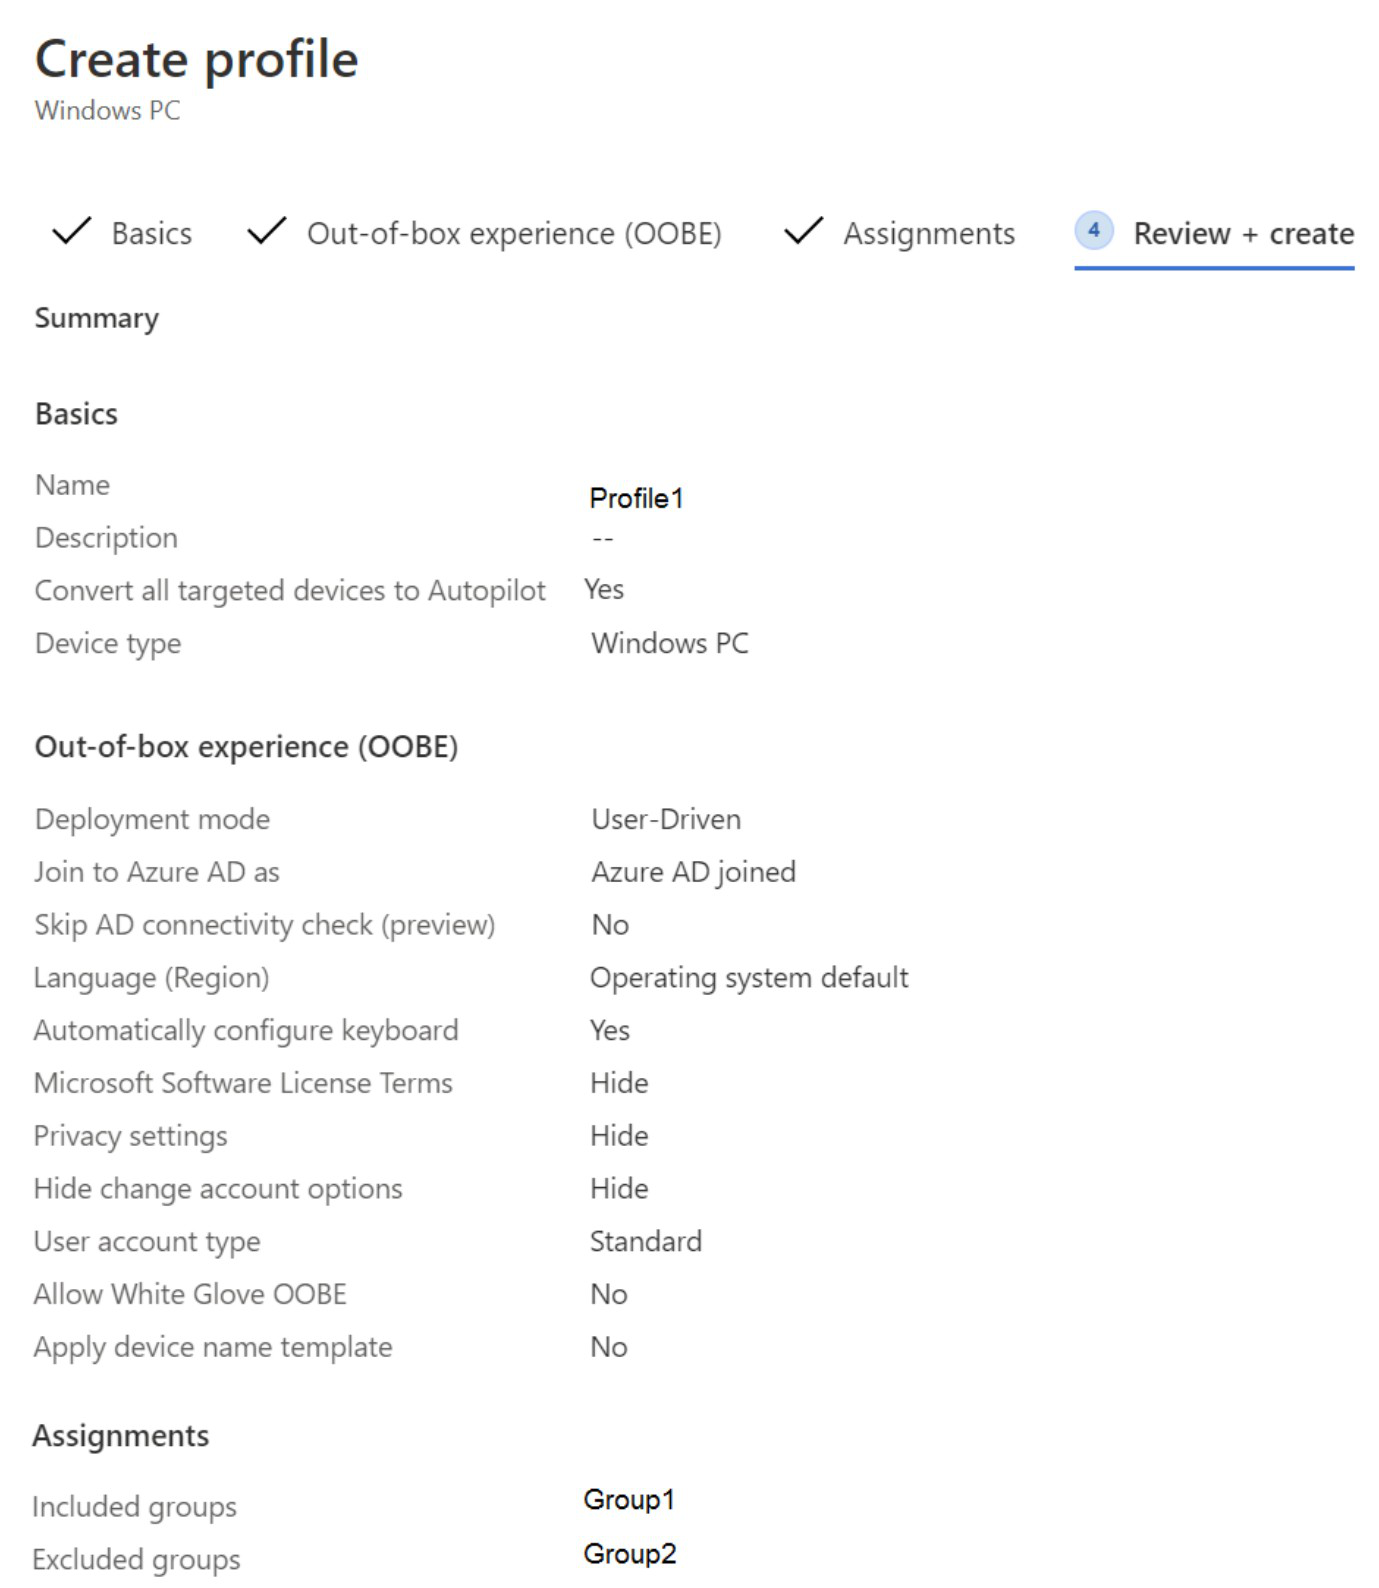
CASE STUDY Overview ADatum Corporation is a consulting company that has a main office in Montreal and branch offices in Seattle and New York. ADatum has a Microsoft 365 E5 subscription. Environment Network Environment The network contains an on-premises Active Directory domain named adatum.com. The domain contains the servers shown in the following table. ADatum has a hybrid Azure AD tenant named adatum.com. Users and Groups The adatum.com tenant contains the users shown in the following table. All users are assigned a Microsoft Office 365 license and an Enterprise Mobility + Security E3 license. Enterprise State Roaming is enabled for Group1 and GroupA. Group1 and Group2 have a Membership type of Assigned. Devices ADatum has the Windows 10 devices shown in the following table. The Windows 10 devices are joined to Azure AD and enrolled in Microsoft Intune. The Windows 10 devices are configured as shown in the following table. All the Azure AD joined devices have an executable file named C:AppA.exe and a folder named D:Folder1. Microsoft Intune Configuration Microsoft Intune has the compliance policies shown in the following table. The Automatic Enrollment settings have the following configurations: • MDM user scope: GroupA • MAM user scope: GroupB You have an Endpoint protection configuration profile that has the following Controlled folder access settings: • Name: Protection1 • Folder protection: Enable List of apps that have access to protected folders: C:*AppA.exe List of additional folders that need to be protected: D:Folder1 Assignments: • Included groups: Group2, GroupB • Windows Autopilot Configuration ADatum has a Windows Autopilot deployment profile configured as shown in the following exhibit. Currently, there are no devices deployed by using Windows Autopilot. The Intune connector for Active Directory is installed on Server1. Requirements Planned Changes ADatum plans to implement the following changes: Purchase a new Windows 10 device named Device6 and enroll the device in Intune New computers will be deployed by using Windows Autopilot and will be hybrid Azure AD joined. Deployed a network boundary configuration profile that will have the following settings: • Name: Boundary1 • Network boundary: 192.168.1.0/24 • Scope tags: Tag1 Assignments: Included groups: Group1, Group2 - Deploy two VPN configuration profiles named Connection1 and Connection2 that will have the following settings: • Name: Connection1 • Connection name: VPN1 • Connection type: L2TP Assignments: Included groups: Group1, Group2, GroupA Excluded groups: -- Name: Connection2 - Connection name: VPN2 - Connection type: IKEv2 - Assignments: • Included groups: GroupA • Excluded groups: GroupB • Technical Requirements ADatum must meet the following technical requirements: Users in GroupA must be able to deploy new computers. Administrative effort must be minimized. Which devices are registered by using the Windows Autopilot deployment service?

Exhibit for question 1

Exhibit for question 1

Exhibit for question 1

Exhibit for question 1

Exhibit for question 1

Exhibit for question 1

Exhibit for question 1

  1. Device1 only
  2. Device3 only
  3. Device1 and Device3 only
  4. Device1, Device2, and Device3 ✅Correct Answer: A, Device1 only Profile1 is assigned with Group1 included and Group2 excluded, and Convert all targeted devices to Autopilot is set to Yes. Conversion applies only to corporate-owned devices that are targeted by the assignment. Device1 is corporate-owned and a member of Group1, so it is registered with Windows Autopilot. Device2 is corporate-owned and in Group1, but it is also in Group2, and an exclusion always wins over an inclusion, so it is not targeted. Device3 and Device4 are personally owned, and Device5 belongs only to Group3, which the profile does not target. Device6 has not been purchased yet, so it is not registered.
Show answer and explanation

The answer and explanation for this question are in the free sample PDF.

Question 2

CASE STUDY Overview ADatum Corporation is a consulting company that has a main office in Montreal and branch offices in Seattle and New York. ADatum has a Microsoft 365 E5 subscription. Environment Network Environment The network contains an on-premises Active Directory domain named adatum.com. The domain contains the servers shown in the following table. ADatum has a hybrid Azure AD tenant named adatum.com. Users and Groups The adatum.com tenant contains the users shown in the following table. All users are assigned a Microsoft Office 365 license and an Enterprise Mobility + Security E3 license. Enterprise State Roaming is enabled for Group1 and GroupA. Group1 and Group2 have a Membership type of Assigned. Devices ADatum has the Windows 10 devices shown in the following table. The Windows 10 devices are joined to Azure AD and enrolled in Microsoft Intune. The Windows 10 devices are configured as shown in the following table. All the Azure AD joined devices have an executable file named C:AppA.exe and a folder named D:Folder1. Microsoft Intune Configuration Microsoft Intune has the compliance policies shown in the following table. The Automatic Enrollment settings have the following configurations: • MDM user scope: GroupA • MAM user scope: GroupB You have an Endpoint protection configuration profile that has the following Controlled folder access settings: • Name: Protection1 • Folder protection: Enable List of apps that have access to protected folders: C:*AppA.exe List of additional folders that need to be protected: D:Folder1 Assignments: • Included groups: Group2, GroupB • Windows Autopilot Configuration ADatum has a Windows Autopilot deployment profile configured as shown in the following exhibit. Currently, there are no devices deployed by using Windows Autopilot. The Intune connector for Active Directory is installed on Server1. Requirements Planned Changes ADatum plans to implement the following changes: Purchase a new Windows 10 device named Device6 and enroll the device in Intune New computers will be deployed by using Windows Autopilot and will be hybrid Azure AD joined. Deployed a network boundary configuration profile that will have the following settings: • Name: Boundary1 • Network boundary: 192.168.1.0/24 • Scope tags: Tag1 Assignments: Included groups: Group1, Group2 - Deploy two VPN configuration profiles named Connection1 and Connection2 that will have the following settings: • Name: Connection1 • Connection name: VPN1 • Connection type: L2TP Assignments: Included groups: Group1, Group2, GroupA Excluded groups: -- Name: Connection2 - Connection name: VPN2 - Connection type: IKEv2 - Assignments: • Included groups: GroupA • Excluded groups: GroupB • Technical Requirements ADatum must meet the following technical requirements: Users in GroupA must be able to deploy new computers. Administrative effort must be minimized. You implement Boundary1 based on the planned changes. Which devices have a network boundary of 192.168.1.0/24 applied?

Exhibit for question 2

Exhibit for question 2

Exhibit for question 2

Exhibit for question 2

Exhibit for question 2

Exhibit for question 2

Exhibit for question 2

  1. Device2 only
  2. Device3 only
  3. Device1, Device2, and Device5 only
  4. Device1, Device2, Device3, and Device4 only ✅Correct Answer: D, Device1, Device2, Device3, and Device4 only The Boundary1 network boundary profile is assigned to Group1 and Group2 with no excluded groups, so every device that is a member of either group receives the 192.168.1.0/24 boundary. Device1 is a member of Group1, Device2 is a member of Group1 and Group2, Device3 is a member of Group1, and Device4 is a member of Group2, so all four devices have the boundary applied. Device5 is a member of Group3 only, which the profile does not target, so it never receives the setting. Ownership and scope tags do not change policy targeting, since scope tags only control which administrators can see the object.
Show answer and explanation

The answer and explanation for this question are in the free sample PDF.

Question 3

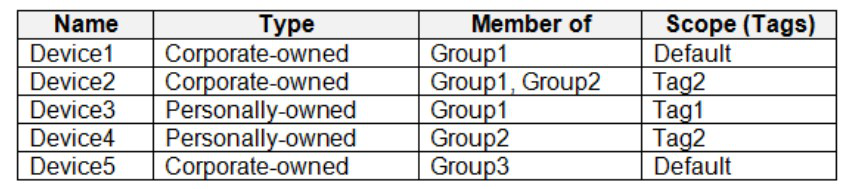
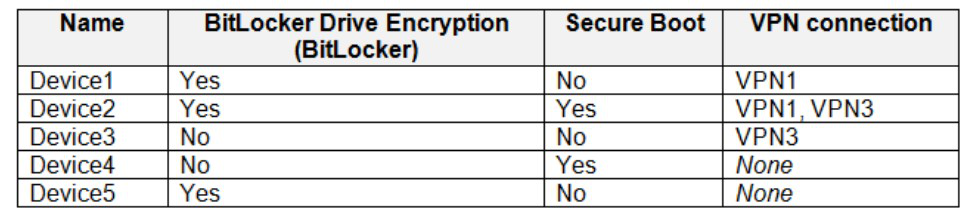
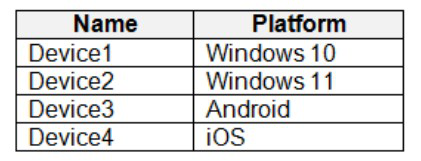
You have devices enrolled in Microsoft Intune as shown in the following table. On which devices can you apply app configuration policies?

Exhibit for question 3

  1. Device2 only
  2. Device1 and Device2 only
  3. Device3 and Device4 only
  4. Device2, Device3, and Device4 only
  5. Device1, Device2, Device3, and Device4
Show answer and explanation

Correct answer: C. Device3 and Device4 only

Intune app configuration policies support only iOS/iPadOS and Android apps, delivering settings to managed apps on those platforms (for enrolled devices or managed apps). Device3 runs Android and Device4 runs iOS, so both can receive them. Windows devices use device configuration profiles, settings catalog policies, or administrative templates instead, so Device1 and Device2 are not eligible.

Why the other options are wrong

  • A. Device2 runs Windows 11, and app configuration policies cannot be assigned to Windows.
  • B. Device1 and Device2 are Windows devices, which these policies do not support.
  • D. Device2 runs Windows 11, an unsupported platform for app configuration policies.
  • E. Windows 10 and Windows 11 are not supported by app configuration policies.

See all 10 free questions Get the full pack, US$39

409 practice questions for Microsoft Endpoint Administrator (MD-102), with full explanations.

Every question comes with the correct answer, the reasoning behind it, and a note on why each wrong option is wrong. Work through it once with the answers, then again with the questions-only copy under exam conditions.

  • 409 questions across all five MD-102 domains
  • Answers and explanations for every question, including the wrong options
  • A questions-only PDF for timed practice runs
  • Instant delivery by email the moment you check out
  • Free monthly updates for as long as the exam is live
  • Pass or your money back

A failed MD-102 attempt costs US$165 in the US, plus the weeks it takes to get ready again. This pack is US$39, paid once, and refunded if you fail.

Try 10 questions free before you buy.

Last updated September 2026 · 409 questions. Aligned to the 24 July 2026 blueprint.

What makes the MD-102 hard

The MD-102 is one of the most scenario-heavy Microsoft Associate exams. It does not test whether you know what Intune is, it puts you inside an enterprise environment and asks what you would actually do.

Enrollment workflows, compliance policies, app protection, device remediation, Autopilot configurations, Defender for Endpoint integration: the decisions a real endpoint administrator makes every day. Candidates who know the tools but have not studied the exam’s question style consistently underperform. Microsoft doesn’t test definitions, it tests decisions.

The blueprint was reorganised on 24 July 2026 into five domains, and it added a dedicated automation, monitoring and reporting domain. Anyone working from notes that still describe a single 40 to 45% “manage, maintain, and protect devices” block is working from a version of the exam that no longer exists.

About the exam

The MD-102 certifies endpoint administrators who deploy, manage and secure devices using Microsoft Intune, Windows Autopilot, Entra ID and Defender for Endpoint across Windows, iOS, Android and macOS. No formal prerequisites. Skills measured as of 24 July 2026. Renews annually via a free Microsoft Learn assessment.

Exam domains

  • Prepare infrastructure for devices: 20 to 25%
  • Manage and maintain devices: 25 to 30%
  • Protect devices: 15 to 20%
  • Manage and secure applications: 15 to 20%
  • Optimize endpoint operations by using automation, monitoring, and reporting: 10 to 15%

40 to 60 questions, 120 minutes, passing score 700 out of 1000, US$165 in the US, priced by local currency elsewhere, online proctored and test centres, renews annually.
Reviews

There are no reviews yet.

Only logged in customers who have purchased this product may leave a review.

Questions before you buy

What do I get when I buy the Microsoft MD-102 pack?

409 practice questions as a PDF, each with the correct answer, a full explanation and a note on why the other options are wrong, plus a separate questions-only PDF for timed practice.

How quickly do I receive it?

Straight away. The full PDF and a questions-only copy are emailed to you the moment your payment goes through, and the same links are on your order page.

Is there a free sample?

Yes. Ten questions from this pack, with answers and explanations, are free on this page and as a PDF, so you can judge the quality before you pay.

Are updates included?

Yes. The pack is updated every month for as long as the exam is live, and updates are free for everyone who has bought it.

What if I fail the exam?

We refund the pack. Sit the exam 7 to 30 days after buying, then send your official score report within 7 days of the exam date, as set out in the refund policy.

Can I share it with colleagues?

Each purchase is licensed to one person. For a team, school or training organisation, email support@certstash.com for a licence that fits.