

FORTINET · NSE4_FGT_AD-7.6

Fortinet NSE4_FGT_AD-7.6 Exam Practice Questions

84 questionsInstant PDF downloadUpdated September 2026

US$39

Try 10 questions free

Card, Apple Pay or Google Pay. Your PDF is sent by email as soon as you check out.

Pass or your money backFail the exam after using this pack and we refund it. How the guarantee works
Category:
TRY BEFORE YOU BUY

Three of the 84 questions in this pack

Question 1

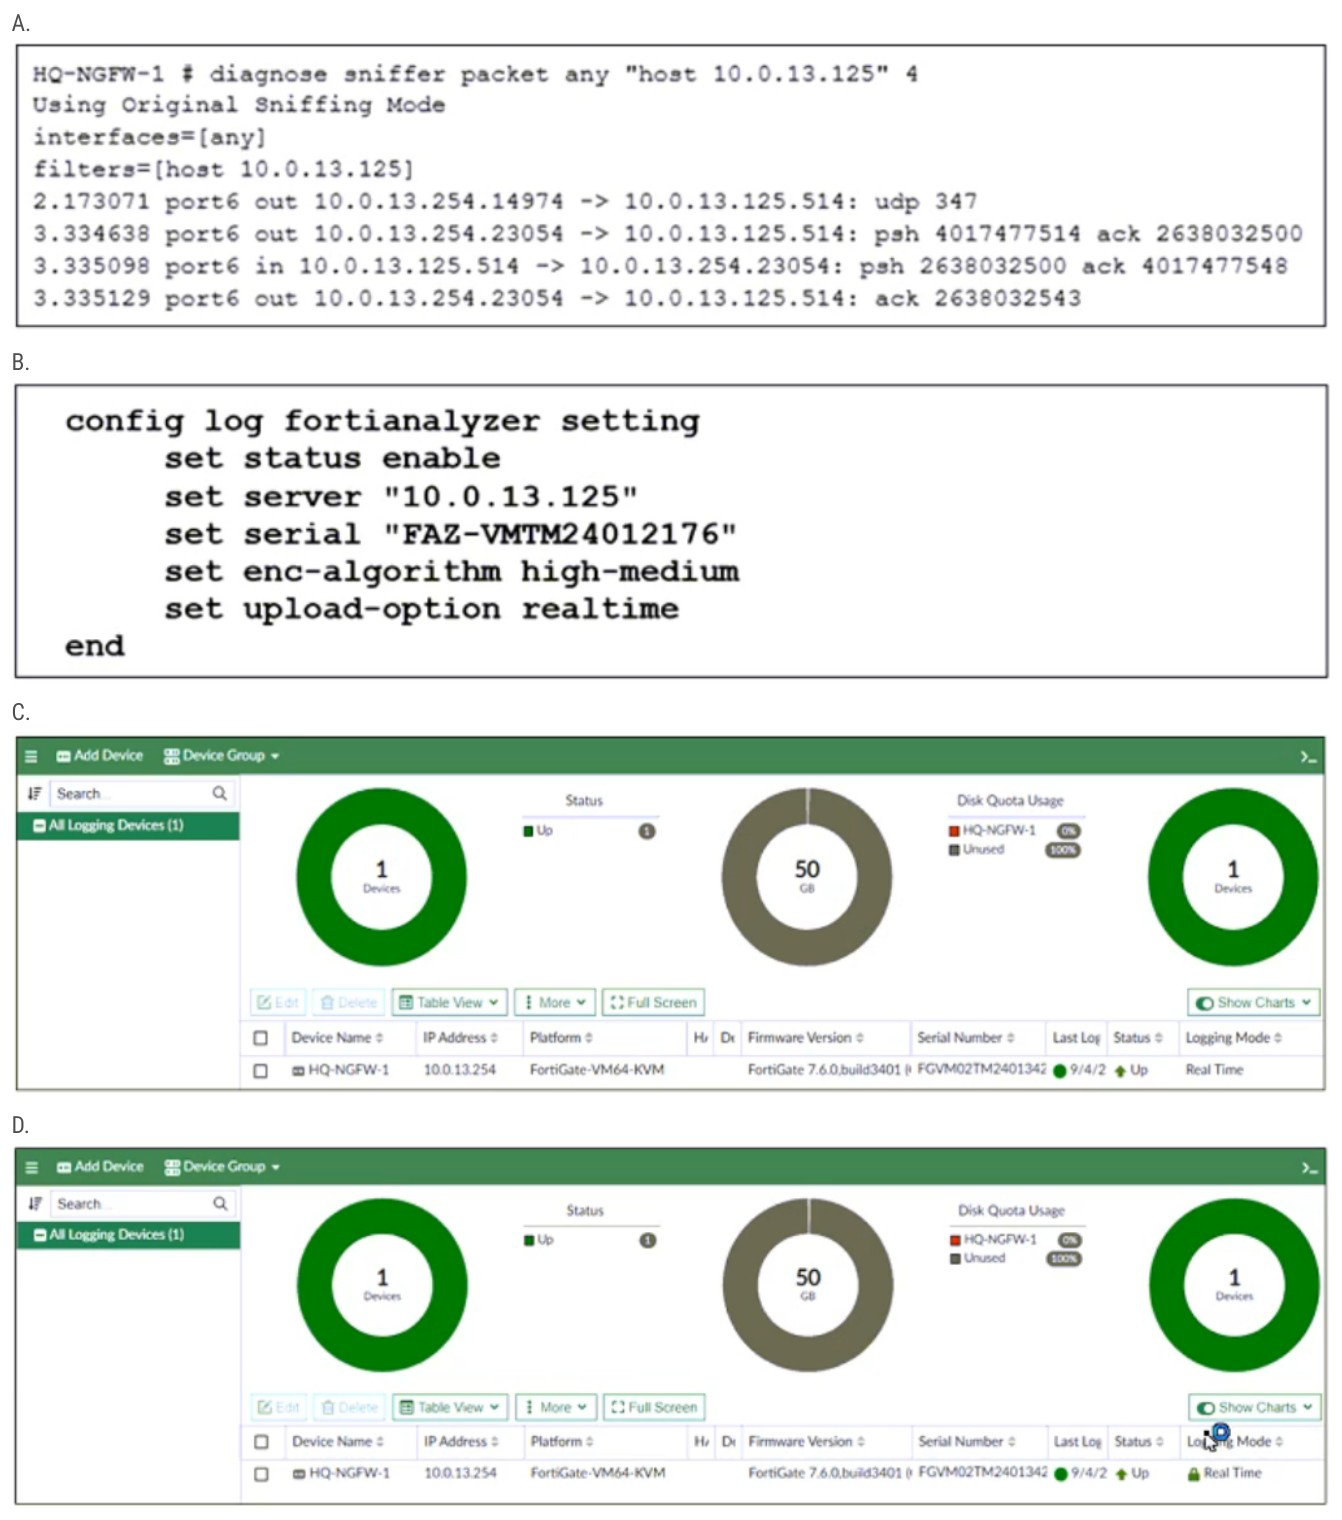
The FortiGate device HQ-NGFW-1 with the IP address 10.0.13.254 sends logs to the FortiAnalyzer device with the IP address 10.0.13.125. The administrator wants to verify that reliable logging is enabled on HQ-NGFW-1.

Which exhibit helps with the verification?

✅Correct Answer: D, FortiGate management interface showing All Logging Devices (1) with device HQ-NGFW-1 at IP 10.0.13.254, FortGate-VM64-KVM

platform, firmware 7.6.0.build3401, serial FGVM02TM24013342, status Up, with a green indicator for Real Time logging mode visible, disk quota usage showing 50 GB

The two FortiAnalyzer Device Manager screens are identical except for one detail: in D the Logging Mode cell for HQ-NGFW-1 at 10.0.13.254 shows Real Time with a padlock. FortiAnalyzer displays that padlock when the log stream arrives over a secured OFTP session, which FortiOS builds only on top of the reliable TCP transport, so it confirms that reliable logging is active on the FortiGate. The administrator can verify the setting from the FortiAnalyzer side without touching the FortiGate CLI, which is exactly what the question asks the exhibit to do.

Exhibit for question 1

Show answer and explanation

The answer and explanation for this question are in the free sample PDF.

Question 2

A network administrator has enabled full SSL inspection and web filtering on FortiGate.

When visiting any HTTPS websites, the browser reports certificate warning errors.

When visiting HTTP websites, the browser does not report errors.

What is the reason for the certificate warning errors?

  1. The matching firewall policy is set to proxy inspection mode.
  2. The option invalid SSL certificates is set to allow on the SSL/SSH inspection profile.
  3. The certificate used by FortiGate for SSL inspection does not contain the required certificate extensions.
  4. The browser does not trust the certificate used by FortiGate for SSL inspection. ✅Correct Answer: D, The browser does not trust the certificate used by FortiGate for SSL inspection. When FortiGate performs full SSL inspection, it re-signs the server certificate with its own CA certificate to decrypt and inspect HTTPS traffic. The browser reports certificate warning errors because that CA is not in its trusted store, so the presented certificate is not issued by a trusted Certificate Authority. Installing the FortiGate CA certificate on the clients removes the warnings. HTTP sites show no errors because that traffic is not encrypted and involves no certificate validation.
Show answer and explanation

Answer and explanation for question 2

Question 3

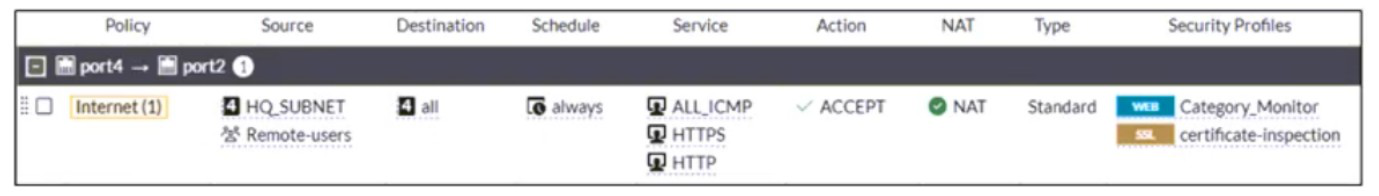
Refer to the exhibit, which shows a firewall policy to enable active authentication.

When attempting to access an external website using an active authentication method, the user is not presented with a login prompt.

What is the most likely reason for this situation?

Exhibit for question 3

  1. The Service DNS is required in the firewall policy.
  2. The Remote-users group is not added to the Destination.
  3. The Remote-users group must be set up correctly in the FSSO configuration.
  4. No matching user account exists for this user.
Show answer and explanation

Correct answer: A. The Service DNS is required in the firewall policy.

The exhibit shows a port4 to port2 policy whose Source is HQ_SUBNET together with the Remote-users group, Destination all, and Service limited to ALL_ICMP, HTTPS and HTTP. Because a user group is referenced in Source, FortiGate will challenge matching HTTP or HTTPS traffic with the captive portal. The problem is that DNS is not in the Service list, so the workstation cannot resolve the external site name. Without a resolved address the browser never generates the HTTP or HTTPS request, FortiGate never sees a session that needs authentication, and no login prompt is displayed. Adding the DNS service, or a separate policy allowing DNS, restores the redirect.

Why the other options are wrong

  • B. User groups are referenced in the Source column, which is exactly where Remote- users already appears in the exhibit; Destination holds addresses and is correctly set to all.
  • C. FSSO is passive authentication and nothing in the exhibit points to an FSSO group; an active authentication policy uses a local or remote user group instead.
  • D. If the account were simply missing, the captive portal page would still be presented and the credentials would then be rejected, so the absence of any prompt is not explained.

See all 10 free questions Get the full pack, US$39

84 practice questions for Fortinet NSE 4, FortiOS 7.6 Administrator (NSE4_FGT_AD-7.6), with full explanations.

Every question comes with the correct answer and a clear explanation. Mapped to the current NSE4_FGT_AD-7.6 exam objectives.

  • 84 questions across all five NSE4_FGT_AD-7.6 domains
  • Answers and explanations for every question, including the wrong options
  • A questions-only PDF for timed practice runs
  • Instant delivery by email the moment you check out
  • Free monthly updates for as long as the exam is live
  • Pass or your money back

A failed NSE 4 attempt costs another US$200, plus the weeks it takes to get ready again. This pack is US$39, paid once, and refunded if you fail anyway.

Try 10 questions free before you buy.

Last updated September 2026 · 84 questions

What makes the NSE 4 hard

If searching for FCP_FGT_AD-7.6, it is the same exam. Fortinet retired the FCF, FCA, FCP, FCSS and FCX names on 15 July 2026 and put the program back on visible NSE 1 to 8 levels. The FortiGate Administrator exam is now NSE 4, FortiOS 7.6 Administrator, registered as NSE4_FGT_AD-7.6, with the same content and blueprint under a new label.

It pays to watch the version, not just the name. Fortinet has NSE 4, FortiOS 8.0 Administrator scheduled for release in mid-September 2026, and Fortinet’s stated practice is that the previous version stays bookable for roughly four months after a new one lands, so anyone studying 7.6 should book it rather than drift into the changeover.

NSE 4 is the entry point to the whole ladder: the FortiManager, FortiAnalyzer and Enterprise Firewall credentials all sit above it, so everything downstream stalls until this one is done.

The exam is not a definition quiz. It leans on configuration extracts, CLI output and troubleshooting scenarios, and content inspection alone is up to 30% of it. This pack has 84 practice questions across all five domains, with every answer explained.

About the exam

NSE 4, FortiOS 7.6 Administrator (NSE4_FGT_AD-7.6) validates the ability to deploy, configure, operate and troubleshoot FortiGate devices in a production network. It is the NSE 4 level of the Fortinet NSE certification program and the standard starting point for the Secure Networking track. It covers FortiOS 7.6.0.

Exam domains

  • Deployment and system configuration: 20 to 25%
  • Firewall policies and authentication: 20 to 25%
  • Content inspection: 25 to 30%
  • Routing: 10 to 15%
  • VPNs: 10 to 15%

50 to 55 questions, 80 to 90 minutes, pass or fail with a score report from the Pearson VUE account, US$200 per attempt, Pearson VUE test centre or online proctored, offered in English and Japanese.
Reviews

There are no reviews yet.

Only logged in customers who have purchased this product may leave a review.

Questions before you buy

What do I get when I buy the Fortinet NSE4_FGT_AD-7.6 pack?

84 practice questions as a PDF, each with the correct answer, a full explanation and a note on why the other options are wrong, plus a separate questions-only PDF for timed practice.

How quickly do I receive it?

Straight away. The full PDF and a questions-only copy are emailed to you the moment your payment goes through, and the same links are on your order page.

Is there a free sample?

Yes. Ten questions from this pack, with answers and explanations, are free on this page and as a PDF, so you can judge the quality before you pay.

Are updates included?

Yes. The pack is updated every month for as long as the exam is live, and updates are free for everyone who has bought it.

What if I fail the exam?

We refund the pack. Sit the exam 7 to 30 days after buying, then send your official score report within 7 days of the exam date, as set out in the refund policy.

Can I share it with colleagues?

Each purchase is licensed to one person. For a team, school or training organisation, email support@certstash.com for a licence that fits.