
10 free Microsoft SC-200 practice questions with the correct answer and a full explanation for each, taken from the CertStash pack of 462 questions. Work through them, then open each answer to check your reasoning.
Get all 462 questions (US$39) · Download these 10 as a PDF
Question 1
You need to receive a security alert when a user attempts to sign in from a location that was never used by the other users in your organization to sign in.
Which anomaly detection policy should you use?
Show answer and explanation
Correct answer: C. Activity from infrequent country
Activity from infrequent country detects when a user signs in from a location/country that is not typical for that user or uncommon across the organization. This is the policy designed to alert on sign-ins from geographically unusual locations that haven't been seen before in your tenant.
Why the other options are wrong
- A. Impossible travel detects when a user travels between distant locations in an impossibly short time period, not about locations never used by other users.
- B. Activity from anonymous IP addresses detects sign-ins from known anonymous proxies or VPNs, not about location frequency within the organization.
- D. Malware detection identifies malicious software, not sign-in location anomalies.
Question 2
You have a Microsoft 365 subscription that uses Microsoft Defender for Office 365.
You have Microsoft SharePoint Online sites that contain sensitive documents. The documents contain customer account numbers that each consists of 32 alphanumeric characters.
You need to create a data loss prevention (DLP) policy to protect the sensitive documents.
What should you use to detect which documents are sensitive?
Show answer and explanation
Correct answer: D. RegEx pattern matching
RegEx pattern matching is the correct method to detect documents containing 32- character alphanumeric patterns (customer account numbers) in DLP policies. DLP uses regex patterns to identify and classify sensitive content for protection rules.
Why the other options are wrong
- A. SharePoint search is a discovery tool but not the mechanism DLP uses to detect sensitive patterns.
- B. Hunting queries in Microsoft 365 Defender are for threat investigation, not for DLP policy creation.
- C. Azure Information Protection is a labeling and classification solution, not the detection method used within DLP policies for pattern matching.
Question 3
Your company uses Microsoft Defender for Endpoint.
The company has Microsoft Word documents that contain macros. The documents are used frequently on the devices of the company's accounting team.
You need to hide false positive in the Alerts queue, while maintaining the existing security posture.
Which three actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
Show answer and explanation
Correct answer: B, D, E
B. Hide the alert. D. Create a suppression rule scoped to a device group. E. Generate the alert. To hide false positives while maintaining security: Hide the alert (B) to remove it from the queue, create a suppression rule scoped to a device group (D) containing the accounting team devices to prevent future similar alerts on those specific devices, and enable/generate the alert mechanism (E) to ensure legitimate threats are still detected. Device group scoping maintains security posture by only suppressing on specific devices.
Why the other options are wrong
- A. Resolving the alert automatically closes it but doesn't prevent future occurrences like a suppression rule does.
- C. Creating a suppression rule scoped to any device would suppress the alert across all devices, reducing security posture.
Question 4
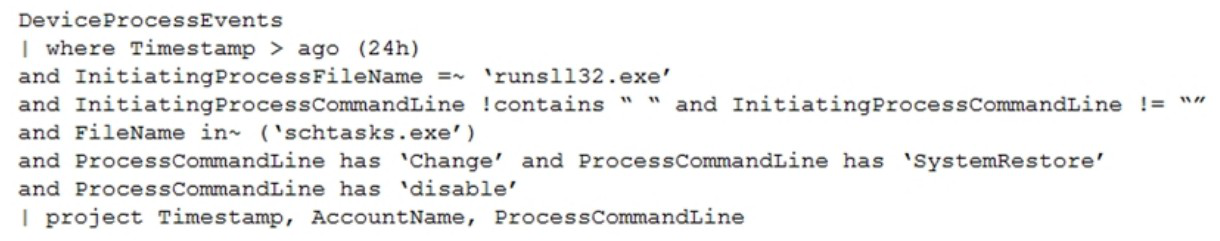
You have the following advanced hunting query in Microsoft 365 Defender.
You need to receive an alert when any process disables System Restore on a device managed by Microsoft Defender during the last 24 hours.
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
Show answer and explanation
Correct answer: A, E
A. Create a detection rule. E. Add DeviceId and ReportId to the output of the query. To receive alerts when processes disable System Restore, you must create a detection rule (A) that will automatically trigger notifications based on the hunting query results. Additionally, you should add DeviceId and ReportId to the query output (E) because these fields are essential for the detection rule to properly identify and track the affected devices and correlate the events with specific reports, enabling actionable alerting and investigation capabilities.
Why the other options are wrong
- B. Suppression rules hide alerts rather than create them; they are used to reduce noise from known benign activities, not to generate alerts.
- C. Ordering by Timestamp is not necessary for creating alerts; the query already filters by timestamp and the order does not affect detection rule functionality.
- D. DeviceNetworkEvents is incorrect because the query is looking for process execution events that disable System Restore, which are process events, not network events.
Question 5
You are investigating a potential attack that deploys a new ransomware strain.
You have three custom device groups. The groups contain devices that store highly sensitive information.
You plan to perform automated actions on all devices.
You need to be able to temporarily group the machines to perform actions on the devices.
Which three actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
Show answer and explanation
Correct answer: A, C, D
A. Assign a tag to the device group. C. Add a tag to the machines. D. Create a new device group that has a rank of 1. To temporarily group machines for automated actions: Create a new device group with rank 1 (D) to establish a temporary grouping for the sensitive devices, add tags to the machines (C) to identify and organize them, and assign a tag to the device group (A) for management purposes. Tags provide flexible temporary organization while device groups with appropriate rank enable automated action scoping.
Why the other options are wrong
- B. Adding device users to admin roles is not necessary for grouping machines.
- E. Creating a new admin role is not required for temporary device grouping.
- F. A rank of 4 is lower priority; rank 1 is higher priority and appropriate for sensitive devices requiring action.
Question 6
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You are configuring Microsoft Defender for Identity integration with Active Directory.
From the Microsoft Defender for identity portal, you need to configure several accounts for attackers to exploit.
Solution: From Entity tags, you add the accounts as Honeytoken accounts.
Does this meet the goal?
Show answer and explanation
Correct answer: A. Yes
Yes, configuring accounts as Honeytoken accounts in the Entity tags section of Microsoft Defender for Identity portal is the correct solution for setting up decoy accounts that attackers will attempt to exploit. Honeytokens are designed to be attractive targets that generate alerts when compromised.
Question 7
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You are configuring Microsoft Defender for Identity integration with Active Directory.
From the Microsoft Defender for identity portal, you need to configure several accounts for attackers to exploit.
Solution: From Azure AD Identity Protection, you configure the sign-in risk policy.
Does this meet the goal?
Show answer and explanation
Correct answer: B. No
No, configuring sign-in risk policy in Azure AD Identity Protection does not meet the goal. Sign-in risk policies respond to detected risky sign-ins but do not configure accounts for attackers to exploit. This is a reactive detection mechanism, not an offensive honeypot configuration.
Question 8
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You are configuring Microsoft Defender for Identity integration with Active Directory.
From the Microsoft Defender for identity portal, you need to configure several accounts for attackers to exploit.
Solution: You add the accounts to an Active Directory group and add the group as a Sensitive group.
Does this meet the goal?
Show answer and explanation
Correct answer: B. No
No, marking an Active Directory group as Sensitive does not configure accounts for attackers to exploit. Sensitive groups designation protects existing important accounts from being compromised, but does not create honeypot accounts designed to attract and detect attackers.
Question 9
You implement Safe Attachments policies in Microsoft Defender for Office 365.
Users report that email messages containing attachments take longer than expected to be received.
You need to reduce the amount of time it takes to deliver messages that contain attachments without compromising security. The attachments must be scanned for malware, and any messages that contain malware must be blocked.
What should you configure in the Safe Attachments policies?
Show answer and explanation
Correct answer: A. Dynamic Delivery
Dynamic Delivery reduces message delivery delays by delivering the message immediately with a placeholder for attachments while they are being scanned in the background. Once scanning completes, the actual attachments are added. This maintains malware protection while improving user experience and delivery speed.
Why the other options are wrong
- B. Replace action substitutes attachments with text warnings but doesn't address delivery speed.
- C. Block and Enable redirect prevents delivery entirely until scanning completes, increasing delay.
- D. Monitor and Enable redirect provides monitoring but doesn't reduce delivery time.
Question 10
You receive a security bulletin about a potential attack that uses an image file.
You need to create an indicator of compromise (IoC) in Microsoft Defender for Endpoint to prevent the attack.
Which indicator type should you use?
Show answer and explanation
That was 10 of 462.
The full Microsoft SC-200 pack has all 462 questions, each with the answer, the explanation and why the other options are wrong, plus a questions-only copy for timed runs. US$39, paid once, with free monthly updates and a pass-or-your-money-back guarantee.