
10 free LPI LPIC-2 202-450 practice questions with the correct answer and a full explanation for each, taken from the CertStash pack of 120 questions. Work through them, then open each answer to check your reasoning.
Get all 120 questions (US$39) · Download these 10 as a PDF
Question 1
On a Linux router, packet forwarding for IPv4 has been enabled. After a reboot, the machine no longer forwards IP packets from other hosts.
The command:
echo 1 > /proc/sys/net/ipv4/ip_forward temporarily resolves this issue.
Which one of the following options is the best way to ensure this setting is saved across system restarts?
Show answer and explanation
Correct answer: C. In /etc/sysct1.conf change net.ipv4.ip_forward to 1
The /etc/sysctl.conf file is the standard configuration file for persistent sysctl settings on Linux systems. Setting net.ipv4.ip_forward = 1 in this file ensures the kernel parameter is applied at boot time through the sysctl service. This is the proper, persistent method endorsed by Linux distributions for maintaining kernel parameters across reboots.
Why the other options are wrong
- A. Login scripts only execute when a user logs in, not at system boot, and root may not always log in.
- B. Relying on user login scripts is unreliable and won't execute if no user logs in after boot.
- D. /etc/rc.local is a shell script, so it needs a command such as sysctl -w net.ipv4.ip_forward=1, not a key = value line.
- E. The iptables-config file is for iptables-specific settings, not general kernel parameters, and the syntax is wrong.
Question 2
What information can be found in the file specified by the status parameter in an OpenVPN server configuration file? (Choose two.)
Show answer and explanation
Correct answer: C, D
C. Statistical information regarding the currently running openvpn daemon D. A list of currently connected clients The OpenVPN status file (specified by the 'status' parameter) contains real-time statistical information about the running OpenVPN daemon, including current connection statistics and performance metrics (option C), and a list of clients currently connected to the server with their connection details (option D). These are the standard contents of the OpenVPN status log.
Why the other options are wrong
- A. Errors and warnings are logged to the main OpenVPN log file, not the status file.
- B. Routing information is not included in the status file; it's maintained by the kernel's routing table.
- E. Historical data about all past connections is not stored in the status file; only current connections are listed.
Question 3
Which of the following lines in the sshd configuration file should, if present, be changed in order to increase the security of the server?
(Choose two.)
Show answer and explanation
Correct answer: A, D
A. Protocol 2, 1 D. PermitRootLogin yes Option A (Protocol 2, 1) should be changed because it enables the insecure SSH protocol version 1; only Protocol 2 should be allowed. Option D (PermitRootLogin yes) should be changed because directly permitting root login via SSH is a significant security risk; it should be set to 'no' to prevent brute-force attacks and direct root compromise. Both represent common security hardening requirements.
Why the other options are wrong
- B. PermitEmptyPasswords no is already the secure setting and requires no change.
- C. While port 22 is the default, changing it is obscurity rather than security and is not required for baseline hardening.
- E. IgnoreRhosts yes is already the secure default setting that should be present.
Question 4
Which of the following nmap parameters scans a target for open TCP ports? (Choose two.)
Show answer and explanation
Correct answer: C, E
C. -sT E. -sS Option C (-sT) performs a TCP connect scan, which completes full TCP connections to open ports. Option E (-sS) performs a SYN scan (half-open scan), which is the most common and stealthy TCP scanning method. Both are legitimate TCP port scanning techniques used to identify open TCP ports on a target.
Why the other options are wrong
- A. -sO is IP protocol scan, not TCP port scanning.
- B. -sZ is SCTP COOKIE ECHO scan, not TCP scanning.
- D. -sU performs UDP scanning, not TCP port scanning.
Question 5
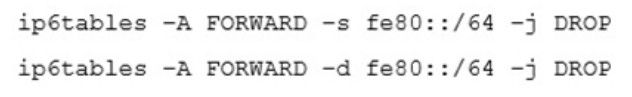
Which of the statements below are correct regarding the following commands, which are executed on a Linux router? (Choose two.)
Show answer and explanation
Correct answer: A, D
A. Packets with source or destination addresses from fe80::/64 will never occur in the FORWARD chain D. Both ip6tables commands complete without an error message or warning The fe80::/64 range contains IPv6 link-local addresses, which are used for local network communication and are never routed across networks. Option A is correct because link- local packets never appear in the FORWARD chain, they are only used for on-link communication and the kernel prevents them from being forwarded. Option D is correct because both commands are syntactically valid: the first uses -s (source) to match packets and the second uses -d (destination) to match packets from the fe80::/64 range; both will execute without error. The rules do not cause forwarding to be disabled globally (B is wrong because routers are identified by unicast addresses in routing tables, not link-local addresses). Option C is incorrect because ip6tables allows multiple rules for the same network in different chains or with different actions. Option E is incorrect because these rules don't suppress router advertisements or DHCPv6, they simply drop matching packets, but DHCPv6 uses other address ranges for communication.
Why the other options are wrong
- B. Routers are identified by unicast or global addresses in routing tables, not link-local addresses from fe80::/64, and these rules do not disable forwarding globally.
- C. ip6tables allows multiple rules targeting the same network address range in different contexts; there is no error for duplicate network specifications.
- E. These rules simply drop packets matching the criteria; they do not suppress router advertisements or DHCPv6 configuration mechanisms, which operate independently.
Question 6
What option in the client configuration file would tell OpenVPN to use a dynamic source port when making a connection to a peer?
Show answer and explanation
Correct answer: D. nobind
The 'nobind' option in OpenVPN client configuration tells the client to not bind to a fixed local port, allowing it to use dynamic source ports when making connections to peers. This is the correct option for enabling dynamic source port allocation in OpenVPN clients.
Why the other options are wrong
- A. src-port is not a valid OpenVPN configuration option.
- B. remote specifies the peer address and port, not the local source port behavior.
- C. source-port is not a valid OpenVPN configuration option.
- E. dynamic-bind is not a valid OpenVPN configuration option.
Question 7
Which Linux user is used by vsftpd to perform file system operations for anonymous FTP users?
Show answer and explanation
Correct answer: E. The Linux user specified in the configuration option ftp_username
ftp_username The vsftpd daemon uses the Linux user specified in the ftp_username configuration option (typically 'ftp') to perform file system operations on behalf of anonymous FTP users. This configuration option explicitly defines which user account vsftpd impersonates when handling anonymous connections, allowing administrators to control file permissions and access.
Why the other options are wrong
- A. The vsftpd process typically runs as root or a dedicated service user, not the user for anonymous operations.
- B. The FTP root directory owner is not necessarily the user used for anonymous operations.
- C. Anonymous users don't have Linux usernames; they're mapped to a single configured user.
- D. vsftpd does not rely on root access with special file permissions for anonymous users; it uses a dedicated ftp user account.
Question 8
Which of the following sshd configuration should be set to no in order to fully disable password based logins? (Choose two.)
Show answer and explanation
Correct answer: B, E
B. ChallengegeResponseAuthentication E. PasswordAuthentication Option B (ChallengeResponseAuthentication) and Option E (PasswordAuthentication) must both be set to 'no' to fully disable password-based logins. ChallengeResponseAuthentication handles keyboard-interactive methods including password prompts, while PasswordAuthentication handles direct password authentication. Disabling both prevents all password-based login methods.
Why the other options are wrong
- A. PAMAuthentication is not a standard sshd configuration option (the correct option is UsePAM).
- C. PermitPlaintextLogin is not a valid sshd configuration option.
- D. UsePasswords is not a valid sshd configuration option.
Question 9
When the default policy for the netfilter INPUT chain is set to DROP, why should a rule allowing traffic to localhost exist?
Show answer and explanation
Correct answer: C. Some applications use the localhost interface to communicate with other applications
communicate with other applications When the INPUT chain policy is DROP, a rule allowing localhost traffic is necessary because many applications use the localhost interface (127.0.0.1 and ::1) to communicate with other local applications or services. Without allowing loopback traffic, essential inter- process communication breaks, causing applications and system services to malfunction. This is a fundamental networking principle that applies regardless of netfilter's specific implementation.
Why the other options are wrong
- A. While true, this is too vague and doesn't explain the specific technical reason why it's necessary.
- B. Netfilter absolutely affects localhost traffic; packets addressed to localhost travel through the network stack and are subject to iptables rules.
- D. While syslogd may use localhost, this is too specific; the general principle applies to many applications.
- E. iptables is a userspace utility; netfilter is the kernel subsystem. The management daemon netfilterd doesn't exist; iptables communicates directly with the kernel.
Question 10
The content of which local file has to be transmitted to a remote SSH server in order to be able to log into the remote server using SSH keys?
Show answer and explanation
Correct answer: C. ~/.ssh/id_rsa.pub
To enable SSH key-based login to a remote server, the public key (id_rsa.pub) from the local client must be transmitted and added to the remote server's ~/.ssh/authorized_keys file. The public key is the only component that should be shared with remote systems; it is used by the server to verify that the client possesses the corresponding private key.
Why the other options are wrong
- A. authorized_keys is the destination file on the remote server where the public key is placed, not the file to be transmitted from the local client.
- B. config is a local SSH client configuration file that specifies connection preferences and has no role in key authentication.
- D. id_rsa is the private key and must never be transmitted or shared with any remote system.
- E. known_hosts stores fingerprints of remote servers the client has connected to, unrelated to authentication key setup.
That was 10 of 120.
The full LPI LPIC-2 202-450 pack has all 120 questions, each with the answer, the explanation and why the other options are wrong, plus a questions-only copy for timed runs. US$39, paid once, with free monthly updates and a pass-or-your-money-back guarantee.