
10 free Cisco 300-415 ENSDWI practice questions with the correct answer and a full explanation for each, taken from the CertStash pack of 502 questions. Work through them, then open each answer to check your reasoning.
Get all 502 questions (US$39) · Download these 10 as a PDF
Question 1
Which component of the Cisco SD-WAN architecture oversees the control plane of overlay network to establish, adjust, and maintain the connections between the WAN Edge devices that form the Cisco SD-WAN fabric?
Show answer and explanation
Correct answer: B. vSmart
The vSmart controller is responsible for overseeing the control plane of the SD-WAN overlay network. It establishes, adjusts, and maintains connections between WAN Edge devices by distributing policies and ensuring proper fabric formation. APIC-EM is a legacy management platform, vManage handles management and monitoring functions, and vBond facilitates initial authentication and NAT traversal rather than controlling the overlay connections.
Why the other options are wrong
- A. APIC-EM is a legacy Cisco management platform, not part of the modern SD-WAN control plane architecture.
- C. vManage is the management plane component responsible for configuration, monitoring, and analytics, not control plane overlay management.
- D. vBond is an orchestration component that facilitates NAT traversal and initial device onboarding, not the primary control plane controller.
Question 2
Which two hardware platforms support Cisco IOS XE SD-WAN images? (Choose two.)
Show answer and explanation
Correct answer: A, E
A. ISR4000 series E. ASR1000 series The ISR 4000 series and ASR 1000 series are Cisco IOS XE routers that can be loaded with the IOS XE SD-WAN image and onboarded as WAN Edge devices in the overlay. Both platforms appear in the Cisco SD-WAN device compatibility matrix alongside the Catalyst 8000 family and ISR 1000 series. Platforms running other operating systems, such as Viptela OS or IOS XR, cannot run an IOS XE SD-WAN image.
Why the other options are wrong
- B. There is no ISR 9300 router series in the Cisco portfolio, so it cannot be a supported IOS XE SD-WAN platform.
- C. vEdge-1000 appliances run Viptela OS, now called Cisco SD-WAN OS, and use the vEdge software image rather than IOS XE.
- D. The ASR 9000 series is a service provider aggregation platform running IOS XR, which has no SD-WAN edge image.
Question 3
What is a default protocol for control plane connection?
Show answer and explanation
Correct answer: D. DTLS
DTLS (Datagram Transport Layer Security) is the default protocol used for control plane connections in Cisco SD-WAN. DTLS provides secure, encrypted communication over UDP and is preferred for WAN environments where packet loss and latency are concerns. While TLS is related, it operates over TCP; HTTPS is an application layer protocol; and IPsec is used for data plane encryption between WAN Edge devices, not for control plane signaling.
Why the other options are wrong
- A. HTTPS operates over TCP at the application layer and is not the default control plane protocol.
- B. TLS operates over TCP and is less suitable for WAN control plane traffic compared to DTLS over UDP.
- C. IPsec is used for encrypting data plane traffic between WAN Edge devices, not for control plane communication.
Question 4
Which component of the Cisco SD-WAN control plane architecture should be located in a public Internet address space and facilitates NAT-traversal?
Show answer and explanation
Correct answer: C. vBond
The vBond controller must be located in public Internet address space and serves as an orchestrator that facilitates NAT traversal for all SD-WAN components. It enables devices behind NAT to establish connections by providing a publicly accessible rendezvous point. WAN Edge devices connect to vBond first, vSmart controllers manage overlay policies, and vManage handles management functions, none of which require or prioritize public Internet placement for NAT traversal.
Why the other options are wrong
- A. WAN Edge devices are located at branch or site edges and do not require public Internet address space for NAT traversal purposes.
- B. vSmart controllers manage control plane policies and can operate in private address space; they are not primarily responsible for NAT traversal.
- D. vManage is the management plane controller and operates in a management network; it is not involved in NAT traversal facilitation.
Question 5
Which Cisco SD-WAN WAN Edge platform supports LTE and Wi-Fi?
Show answer and explanation
Correct answer: A. ISR 1101
The ISR 1101 is a Cisco WAN Edge platform that supports both LTE and Wi-Fi connectivity, making it suitable for branch deployments requiring multiple WAN access options. The ASR 1001 is a router without integrated wireless, the CSR 1000v is a virtual appliance lacking physical wireless interfaces, and the vEdge 2000 is an appliance-based platform without LTE or Wi-Fi support.
Why the other options are wrong
- B. ASR 1001 is a fixed router platform without integrated LTE or Wi-Fi capability.
- C. CSR 1000v is a virtual router and cannot provide LTE or Wi-Fi connectivity.
- D. vEdge 2000 is a hardware appliance designed for fixed WAN connectivity without LTE or Wi-Fi support.
Question 6
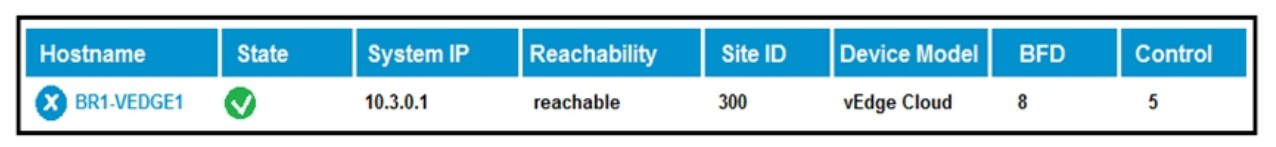
Refer to the exhibit.
What does the BFD value of 8 represent?
Show answer and explanation
Correct answer: D. number of BFD sessions
The exhibit is the vManage device list, where the BFD column reports how many BFD sessions the WAN Edge currently has in the up state, and the Control column reports the number of established control connections. BR1-VEDGE1 therefore has 8 BFD sessions to remote TLOCs and 5 control connections. A WAN Edge builds one BFD session per local TLOC to remote TLOC color pair, so counts well above one are normal.
Why the other options are wrong
- A. The device table does not display a dead timer, and BFD failure detection is derived from the hello interval multiplied by the detect multiplier inside the session details.
- B. The BFD app-route poll interval is a configured timer under BFD settings and is not reported in this summary column.
- C. The BFD hello interval defaults to 1000 ms per session and is shown in the BFD session detail view, not as this device level value.
Question 7
A network administrator is bringing up one WAN Edge router for branch connectivity.
Which types of tunnels form when the WAN edge router connects to the Cisco SD-WAN fabric?
Show answer and explanation
Correct answer: D. DTLS or TLS tunnel with vSmart controller and IPsec tunnel with other WAN Edge routers
tunnel with other WAN Edge routers When a WAN Edge router joins the SD-WAN fabric, it establishes a DTLS or TLS tunnel with the vSmart controller for control plane signaling and policy distribution, and an IPsec tunnel with other WAN Edge routers in the fabric for secure data plane traffic. The vBond controller uses DTLS for initial authentication but is not part of ongoing tunnel maintenance, vManage is not involved in data plane tunnels, and the initial connection to vBond precedes vSmart connection.
Why the other options are wrong
- A. While DTLS or TLS connects to vSmart, IPsec tunnels are formed with other WAN Edge routers, not with vBond.
- B. DTLS or TLS connects to vBond only initially for authentication; ongoing control plane uses vSmart, and IPsec tunnels are with other edges, not vManage.
- C. The control plane tunnel is with vSmart, not vBond, and IPsec data plane tunnels connect to other WAN Edge routers.
Question 8
If Smart Account Sync is not used, which Cisco SD-WAN component is used to upload an authorized serial number file?
Show answer and explanation
Correct answer: D. vManage
The vManage controller is used to upload authorized serial number files when Smart Account Sync is not implemented. This manual upload process allows administrators to authorize specific WAN Edge devices by their serial numbers, enabling them to join the SD-WAN fabric. WAN Edge devices cannot perform uploads, vSmart handles policy control, and vBond handles initial onboarding and authentication but not file uploads.
Why the other options are wrong
- A. WAN Edge devices are clients that cannot upload files to the management system.
- B. vSmart is a control plane component focused on policy distribution, not device authorization file management.
- C. vBond facilitates initial authentication but does not provide the interface for uploading serial number authorization files.
Question 9
Which port is used for vBond under controller certificates if no alternate port is configured?
Show answer and explanation
Correct answer: D. 12346
Port 12346 is the default port used by vBond under controller certificates when no alternate port is configured. This port is used for secure communication between WAN Edge devices and the vBond orchestrator during the initial authentication and bootstrapping phase. The other port numbers listed are not associated with vBond's default configuration.
Why the other options are wrong
- A. Port 12344 is not the standard vBond controller certificate port.
- B. Port 12345 is not the standard vBond controller certificate port.
- C. Port 12347 is not the standard vBond controller certificate port.
Question 10
In the Cisco SD-WAN solution, vSmart controller is responsible for which two actions? (Choose two.)
Show answer and explanation
Correct answer: C, E
C. Distribute route and policy information via OMP. E. Distribute crypto key information among WAN Edge routers. The vSmart controller is the control plane of the fabric: it peers with every WAN Edge over OMP and advertises OMP routes, TLOCs, service routes and centralized policy. It also acts as the key exchange point, receiving each WAN Edge IPsec encryption key and redistributing it to authorized peers so data plane tunnels can form without a full mesh of IKE sessions. Device configuration and monitoring belong to vManage, and initial orchestration and NAT discovery belong to vBond.
Why the other options are wrong
- A. Initial authentication and authorization of a WAN Edge into the overlay is performed by the vBond orchestrator when the device first calls home.
- B. Configuration templates, software upgrades and monitoring of WAN Edge routers are vManage management plane functions.
- D. vSmart plays no role in DHCP address assignment, which is handled locally at the site or by a separate DHCP server.
That was 10 of 502.
The full Cisco 300-415 ENSDWI pack has all 502 questions, each with the answer, the explanation and why the other options are wrong, plus a questions-only copy for timed runs. US$39, paid once, with free monthly updates and a pass-or-your-money-back guarantee.