Popular
COMPTIA · CS0-003

CompTIA CySA+ CS0-003 Exam Practice Questions

627 questionsInstant PDF downloadUpdated September 2026

US$39

Try 10 questions free

Card, Apple Pay or Google Pay. Your PDF is sent by email as soon as you check out.

Pass or your money backFail the exam after using this pack and we refund it. How the guarantee works
Category:
TRY BEFORE YOU BUY

Three of the 627 questions in this pack

Question 1

A recent zero-day vulnerability is being actively exploited, requires no user interaction or privilege escalation, and has a significant impact to confidentiality and integrity but not to availability. Which of the following CVE metrics would be most accurate for this zero-day threat?

  1. CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:N
  2. CVSS:3.1/AV:N/AC:L/PR:H/UI:R/S:C/C:H/I:H/A:L
  3. CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:L/I:H/A:H
  4. CVSS:3.1/AV:L/AC:L/PR:L/UI:R/S:U/C:H/I:L/A:H
Show answer and explanation

Correct answer: A. CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:N

The described threat is remotely exploitable, needs no privileges and no user interaction, and impacts confidentiality and integrity heavily while leaving availability untouched. Option A maps exactly to that profile: AV:N (network attack vector, consistent with active remote exploitation), AC:L (low complexity, as seen with a zero-day being exploited at scale), PR:N (no privilege escalation required), UI:N (no user interaction), S:U (unchanged scope), C:H and I:H (significant confidentiality and integrity loss), and A:N (no availability impact). No other vector combines all of these values.

Why the other options are wrong

  • B. It requires high privileges (PR:H) and user interaction (UI:R), and it lists an availability impact (A:L), contradicting the scenario.
  • C. It requires user interaction (UI:R), understates confidentiality loss (C:L), and adds a high availability impact the scenario says does not exist.
  • D. It restricts the attack to local access (AV:L), requires privileges and user interaction, and shows high availability impact with only low integrity impact.

Question 2

Which of the following tools would work best to prevent the exposure of PII outside of an organization?

  1. PAM
  2. IDS
  3. PKI
  4. DLP
Show answer and explanation

Correct answer: D. DLP

Data Loss Prevention (DLP) is specifically designed to monitor, detect, and prevent unauthorized transmission of sensitive information including PII outside organizational boundaries. DLP tools scan data in motion and at rest to enforce policies against exfiltration. PAM manages privileged access, IDS detects intrusions, and PKI manages encryption, none are designed to specifically prevent PII exposure.

Why the other options are wrong

  • A. PAM controls privileged account access but doesn't prevent data exfiltration
  • B. IDS detects network intrusions but doesn't prevent sensitive data disclosure
  • C. PKI manages certificates and encryption but doesn't monitor for data exposure

Question 3

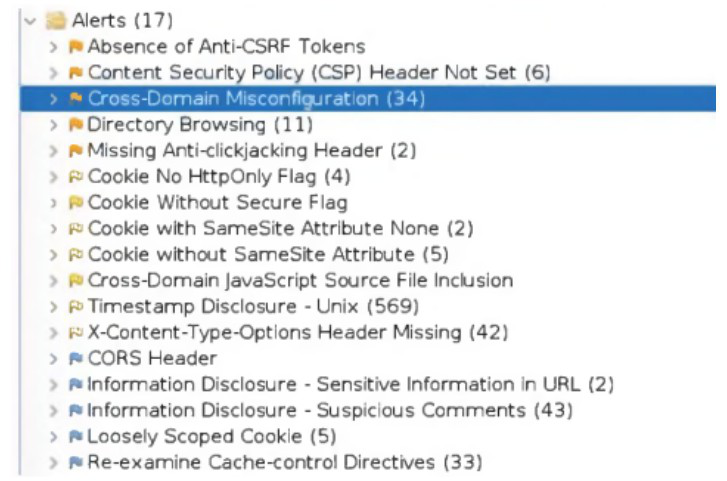
An organization conducted a web application vulnerability assessment against the corporate website, and the following output was observed: Which of the following tuning recommendations should the security analyst share?

Exhibit for question 3

  1. Set an HttpOnly flag to force communication by HTTPS
  2. Block requests without an X-Frame-Options header
  3. Configure an Access-Control-Allow-Origin header to authorized domains
  4. Disable the cross-origin resource sharing header
Show answer and explanation

Correct answer: C. Configure an Access-Control-Allow-Origin header to authorized domains

authorized domains The assessment results show 'Cross-Domain Misconfiguration (34)' as a critical alert, indicating improper handling of cross-origin requests. The proper remediation for cross- domain issues is to configure the Access-Control-Allow-Origin header to specify only authorized domains, which controls which origins can access resources and prevents unauthorized cross-domain access. This directly addresses the misconfiguration vulnerability without blocking legitimate cross-domain communication.

Why the other options are wrong

  • A. HttpOnly flag is for cookies and HTTPS is enforced by Strict-Transport-Security; this doesn't address cross-domain misconfiguration issues.
  • B. X-Frame-Options prevents clickjacking (separate alert exists for missing anti- clickjacking header) and doesn't resolve cross-domain misconfiguration.
  • D. Disabling CORS entirely is overly restrictive; the proper fix is to configure it correctly for authorized domains rather than disable it completely.

See all 10 free questions Get the full pack, US$39

627 practice questions for CompTIA CySA+ (CS0-003), with full explanations.

Every question comes with the correct answer, a clear explanation, and a note on why each other option is wrong. Mapped to the current CS0-003 objectives.

  • 627 questions, MCQs and PBQs, mapped to the CS0-003 objectives
  • Answers and explanations for every question, including the wrong options
  • A questions-only PDF for timed practice runs
  • Instant delivery by email the moment you check out
  • Free monthly updates for as long as the exam is live
  • Pass or your money back

A failed CS0-003 attempt costs the full US$439 voucher again. This pack is US$39, paid once, and refunded if you fail.

Try 10 questions free before you buy.

Last updated September 2026 · 627 questions

What makes the CySA+ CS0-003 hard

Sitting the exam after December 2026? You want CS0-004 instead: CompTIA retires the English CS0-003 exam on 22 December 2026 (translated versions 23 March 2027). This pack is for candidates booked on CS0-003 before those dates.

CySA+ is not the kind of exam you can get through on general security knowledge. It is a scenario-heavy, analyst-focused exam that tests your ability to interpret SIEM output, triage alerts, prioritise vulnerabilities and walk through an incident response, not just define the concepts. Performance-based questions put you in simulated SOC environments and ask you to make the call.

The candidates who fail CySA+ are usually experienced security professionals who underestimated how specifically CompTIA frames its analyst scenarios. Knowing the MITRE ATT&CK framework is not the same as knowing how CS0-003 asks about it, and this pack has 627 practice questions built around exactly that framing.

About the exam

The CompTIA CySA+ is CompTIA’s intermediate-level cybersecurity certification, sitting between Security+ and SecurityX. It validates the ability to detect, analyse and respond to threats through continuous security monitoring, covering security operations, vulnerability management, incident response and reporting. DoD 8140 approved across multiple analyst and responder work roles including SOC analyst, threat intelligence analyst and vulnerability assessment analyst. Four years of hands-on security experience is recommended. CS0-003 is the V3 exam: the English learning products retire 22 November 2026, the English exam retires 22 December 2026, and the Japanese, Portuguese and Spanish exams retire 23 March 2027. The replacement is CS0-004 (V4), which launched 23 June 2026.

Exam domains

  • Security operations: 33%
  • Vulnerability management: 30%
  • Incident response management: 20%
  • Reporting and communication: 17%

Up to 85 questions including PBQs, 165 minutes, pass mark 750 out of 900, US$439 per voucher, Pearson VUE testing centres or online proctored, valid for three years.
Reviews

There are no reviews yet.

Only logged in customers who have purchased this product may leave a review.

Questions before you buy

What do I get when I buy the CompTIA CySA+ CS0-003 pack?

627 practice questions as a PDF, each with the correct answer, a full explanation and a note on why the other options are wrong, plus a separate questions-only PDF for timed practice.

How quickly do I receive it?

Straight away. The full PDF and a questions-only copy are emailed to you the moment your payment goes through, and the same links are on your order page.

Is there a free sample?

Yes. Ten questions from this pack, with answers and explanations, are free on this page and as a PDF, so you can judge the quality before you pay.

Are updates included?

Yes. The pack is updated every month for as long as the exam is live, and updates are free for everyone who has bought it.

What if I fail the exam?

We refund the pack. Sit the exam 7 to 30 days after buying, then send your official score report within 7 days of the exam date, as set out in the refund policy.

Can I share it with colleagues?

Each purchase is licensed to one person. For a team, school or training organisation, email support@certstash.com for a licence that fits.