
10 free CompTIA SecurityX CAS-005 practice questions with the correct answer and a full explanation for each, taken from the CertStash pack of 475 questions. Work through them, then open each answer to check your reasoning.
Get all 475 questions (US$39) · Download these 10 as a PDF
Question 1
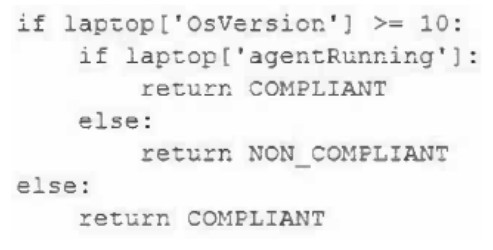
A security engineer is reviewing event logs because an employee successfully connected a personal Windows laptop to the corporate network, which is against company policy. Company policy allows all Windows 10 and 11 laptops to connect to the system as long as the MDM agent installed by IT is running. Only compliant devices can connect, and the logic in the system to evaluate compliant laptops is as follows:
Which of the following most likely occurred when the employee connected a personally owned Windows laptop and was allowed on the network?
Show answer and explanation
The answer and explanation for this question are in the free sample PDF.
Question 2
An organization is working to secure its development process to ensure developers cannot deploy artifacts directly into the production environment.
Which of the following security practice recommendations would be the best to accomplish this objective?
Show answer and explanation
Correct answer: C. Set up policies and systems with separation of duties.
Separation of duties is a fundamental access control principle that prevents any single individual from having complete control over a critical transaction or process. By implementing policies and systems with separation of duties, the organization ensures that developers cannot unilaterally deploy artifacts to production, this requires approval and execution by different roles. This directly addresses the stated objective of preventing direct production deployments by developers.
Why the other options are wrong
- A. Least privilege access is important but doesn't specifically prevent developers from deploying to production if they have any production access.
- B. Security awareness training improves security culture but doesn't enforce technical controls preventing direct deployments.
- D. Job rotation reduces insider threat risk over time but doesn't prevent current deployment capabilities.
- E. Mandatory vacations may help detect fraudulent activities but don't prevent unauthorized deployments.
- F. Quarterly access reviews are detective controls that occur too infrequently to prevent unauthorized deployments.
Question 3
A security architect discovers the following while reviewing code for a company's website: selection = "SELECT Item FROM Catalog WHERE ItemID = " & Request("ItemID")
Which of the following should the security architect recommend?
Show answer and explanation
Correct answer: B. Query parameterization
The code is vulnerable to SQL injection because user input from Request('ItemID') is concatenated straight into the query string. Query parameterization, also called prepared statements, sends the SQL structure and the user-supplied values separately, so input is treated as data and never as executable SQL. This is the primary, industry-standard defense against SQL injection.
Why the other options are wrong
- A. Client-side processing can be bypassed by any attacker crafting requests directly, and the injection still executes at the database.
- C. Data normalization organizes how data is stored; it does not separate code from input in a query.
- D. Blocking or escaping characters is a filtering approach that is incomplete and can be bypassed by alternate encodings.
- E. URL encoding only changes how characters are represented in a request; the database still executes the injected SQL.
Question 4
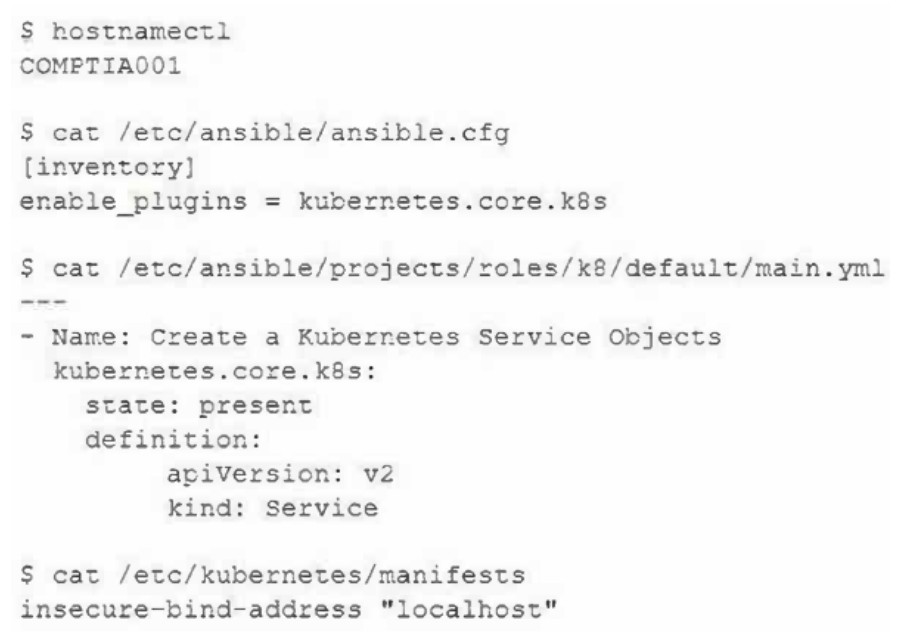
A security architect needs to enable a container orchestrator for DevSecOps and SOAR initiatives. The engineer has discovered that several Ansible YAML files used for the automation of configuration management have the following content:
Which of the following should the engineer do to correct the security issues presented within this content?
Show answer and explanation
The answer and explanation for this question are in the free sample PDF.
Question 5
A CRM company leverages a CSP PaaS service to host and publish Its SaaS product. Recently, a large customer requested that all infrastructure components must meet strict regulatory requirements, including configuration management, patch management, and life-cycle management.
Which of the following organizations is responsible for ensuring those regulatory requirements are met?
Show answer and explanation
Correct answer: A. The CRM company
In a PaaS cloud model, the CRM company (the customer) retains responsibility for application-level security controls and compliance requirements. While the CSP provides infrastructure, the CRM company must ensure that its deployment meets regulatory requirements including configuration management, patch management, and lifecycle management of the application and its data. The customer cannot delegate compliance responsibility to the cloud provider.
Why the other options are wrong
- B. The customer's customer does not have direct responsibility for the infrastructure requirements.
- C. The CSP provides infrastructure but the responsibility for meeting regulatory requirements specific to the customer's business rests with the CRM company.
- D. The regulatory body sets requirements but doesn't implement the controls needed to meet them.
Question 6
Company A is merging with Company B. Company A is a small, local company. Company B has a large, global presence. The two companies have a lot of duplication in their IT systems, processes, and procedures. On the new Chief Information Officer's (CIO's) first day, a fire breaks out at Company B's main data center.
Which of the following actions should the CIO take first?
Show answer and explanation
Correct answer: B. Review the incident response plans, and engage the disaster recovery plan while relying on the IT leaders from both companies.
A fire in a live data center is an active crisis, so the CIO's first action is to work from the plans that already exist: review the incident response plans and activate the disaster recovery plan, using the IT leaders from both companies who know the affected systems. That combination drives immediate containment and recovery while making use of the only people who understand the duplicated environments.
Why the other options are wrong
- A. Checking whether the plans were ever tested is a readiness question, not the first action while a facility is burning.
- C. Confirming site availability and briefing leadership are useful, but they delay activating the recovery process.
- D. A BIA is pre-incident planning that sets recovery priorities, not a first response action during an active fire.
Question 7
The results of an internal audit indicate several employees reused passwords that were previously included in a published list of compromised passwords.
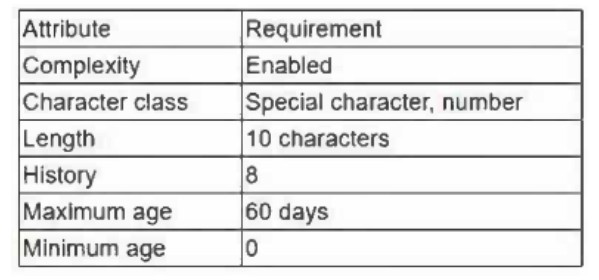
The company has the following employee password policy:
Which of the following should be implemented to best address the password reuse issue? (Choose two.)
Show answer and explanation
The answer and explanation for this question are in the free sample PDF.
Question 8
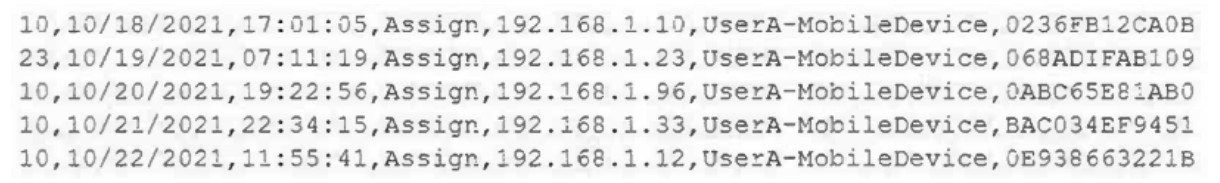
A mobile administrator is reviewing the following mobile device DHCP logs to ensure the proper mobile settings are applied to managed devices:
Which of the following mobile configuration settings is the mobile administrator verifying?
Show answer and explanation
Correct answer: D. Association MAC address randomization
The DHCP logs show multiple assignments to the same user (UserA-MobileDevice) with different MAC addresses over consecutive days (0236FB12CA0B, 068ADIFAB109, 0ABC65E81AB0, BAC034EF9451, 0E938663221B). This pattern of changing MAC addresses for the same device and user is characteristic of MAC address randomization, a privacy feature where devices use different MAC addresses for each DHCP request or network connection to prevent tracking across networks. The administrator would review DHCP logs to verify this security setting is properly configured on managed mobile devices.
Why the other options are wrong
- A. SSID authentication verification would not require analyzing DHCP assignment logs with varying MAC addresses.
- B. Auto-joining wireless networks would not produce a pattern of different MAC addresses assigned to the same user device across multiple days.
- C. 802.1X mutual authentication is an authentication protocol and would not be verified by observing MAC address changes in DHCP logs.
Question 9
A security analyst is investigating a possible insider threat incident that involves the use of an unauthorized USB from a shared account to exfiltrate data. The event did not create an alert. The analyst has confirmed the USB hardware ID is not on the device allow list, but has not yet confirmed the owner of the USB device.
Which of the following actions should the analyst take next?
Show answer and explanation
Correct answer: B. Classify the incident as a false negative.
A false negative occurs when a detection system fails to alert on a malicious event that actually occurred. In this case, an actual incident (unauthorized USB used to exfiltrate data from a shared account) happened but the system did not create an alert. This is a failure of detection controls, the incident was real but undetected by monitoring systems, making it a false negative.
Why the other options are wrong
- A. False positive means alerting on benign activity; this was a confirmed malicious event.
- C. True positive means correctly detecting actual malicious activity with an alert; no alert was generated.
- D. True negative means correctly not alerting on benign activity; this event was confirmed malicious.
Question 10
Which of the following security features do email signatures provide?
Show answer and explanation
Correct answer: A. Non-repudiation
Email signatures provide non-repudiation, which is the assurance that the sender cannot deny having sent the message. A digital signature, created with the sender's private key and verifiable with their public key, cryptographically proves that a specific individual sent the message and that it hasn't been altered. This prevents the signer from later repudiating (denying) having sent the email.
Why the other options are wrong
- B. Email signatures do not encrypt message body content; that requires separate encryption mechanisms.
- C. Code signing is a different application of digital signatures used for software authenticity, not email signatures.
- D. While sender authentication may be a benefit, non-repudiation is the primary security property provided.
- E. Chain of custody refers to evidence handling procedures unrelated to email signatures.
That was 10 of 475.
The full CompTIA SecurityX CAS-005 pack has all 475 questions, each with the answer, the explanation and why the other options are wrong, plus a questions-only copy for timed runs. US$39, paid once, with free monthly updates and a pass-or-your-money-back guarantee.